

If you think compliance is expensive, consider that the cost of failing an audit is now 2.71 times higher than the price of getting it right. This financial risk is why automated compliance scanning software has become a technical necessity in 2026. You likely feel the weight of manual DSAR requests that move too slowly. You probably worry about sensitive data hiding in old email attachments or forgotten network corners. Traditional compliance bloatware often makes the problem worse by adding layers of unnecessary complexity.
You need a way to find data where it lives - without the drama of a massive deployment. This technical guide explains how automated scanning identifies sensitive data across your network to ensure audit readiness without manual effort. We will break down the shift to PCI DSS v4.0.1, the impact of the UK Data (Use and Access) Act 2025, and how to organise a clear inventory of personal data that stands up to scrutiny. Learn how to secure your environment and reduce the risk of GDPR fines through local, efficient discovery.
Key Takeaways
- Replace manual discovery with automated mapping to eliminate human error and organisational oversight risks.
- Use automated compliance scanning software to organise a clear inventory of personal data across all network endpoints.
- Maintain data privacy by adopting local-only scanning - keeping raw files on the device rather than exfiltrating them to the cloud.
- Detect sensitive information in images and scanned documents through integrated OCR technology.
- Prepare for PCI DSS v4.0.1 and GDPR audits with automated evidence that proves exactly where your data lives.
What is automated compliance scanning software?
Finding every piece of sensitive data on your network is no longer a manual task. It is a technical challenge that requires a technical solution. Automated compliance scanning software is a tool that identifies and maps sensitive data across an entire organisation - including laptops, servers, and cloud storage. It builds a live picture of your risk. This software replaces manual data discovery. Manual processes are slow. They are prone to human error. They rely on people remembering where they saved a file. Automated scanning doesn't forget. It checks for specific patterns like credit card numbers or personal data identifiers across every file it touches. Automated compliance scanning is a technical necessity for modern GDPR and PCI DSS adherence.
These tools often align with the Security Content Automation Protocol (SCAP). This provides a standardised framework for enumerating flaws and measuring compliance. By using these standards, scanning software ensures that the evidence it gathers is consistent, verifiable, and ready for an auditor's review. It moves your compliance posture from a best guess to a hard fact.
GRC platforms vs. data discovery tools
Governance, Risk, and Compliance (GRC) platforms manage your policies. They are the what and the why. Data discovery tools are the how. Many GRC tools rely on manual input or basic integrations that only scratch the surface. They tell you that you should have a policy for personal data. Discovery tools provide the technical evidence of where that data actually resides. Whilst a GRC platform might store your GDPR compliance documents, the discovery tool proves you are following them by locating every hidden spreadsheet and forgotten database export.
Why manual data mapping is no longer sufficient
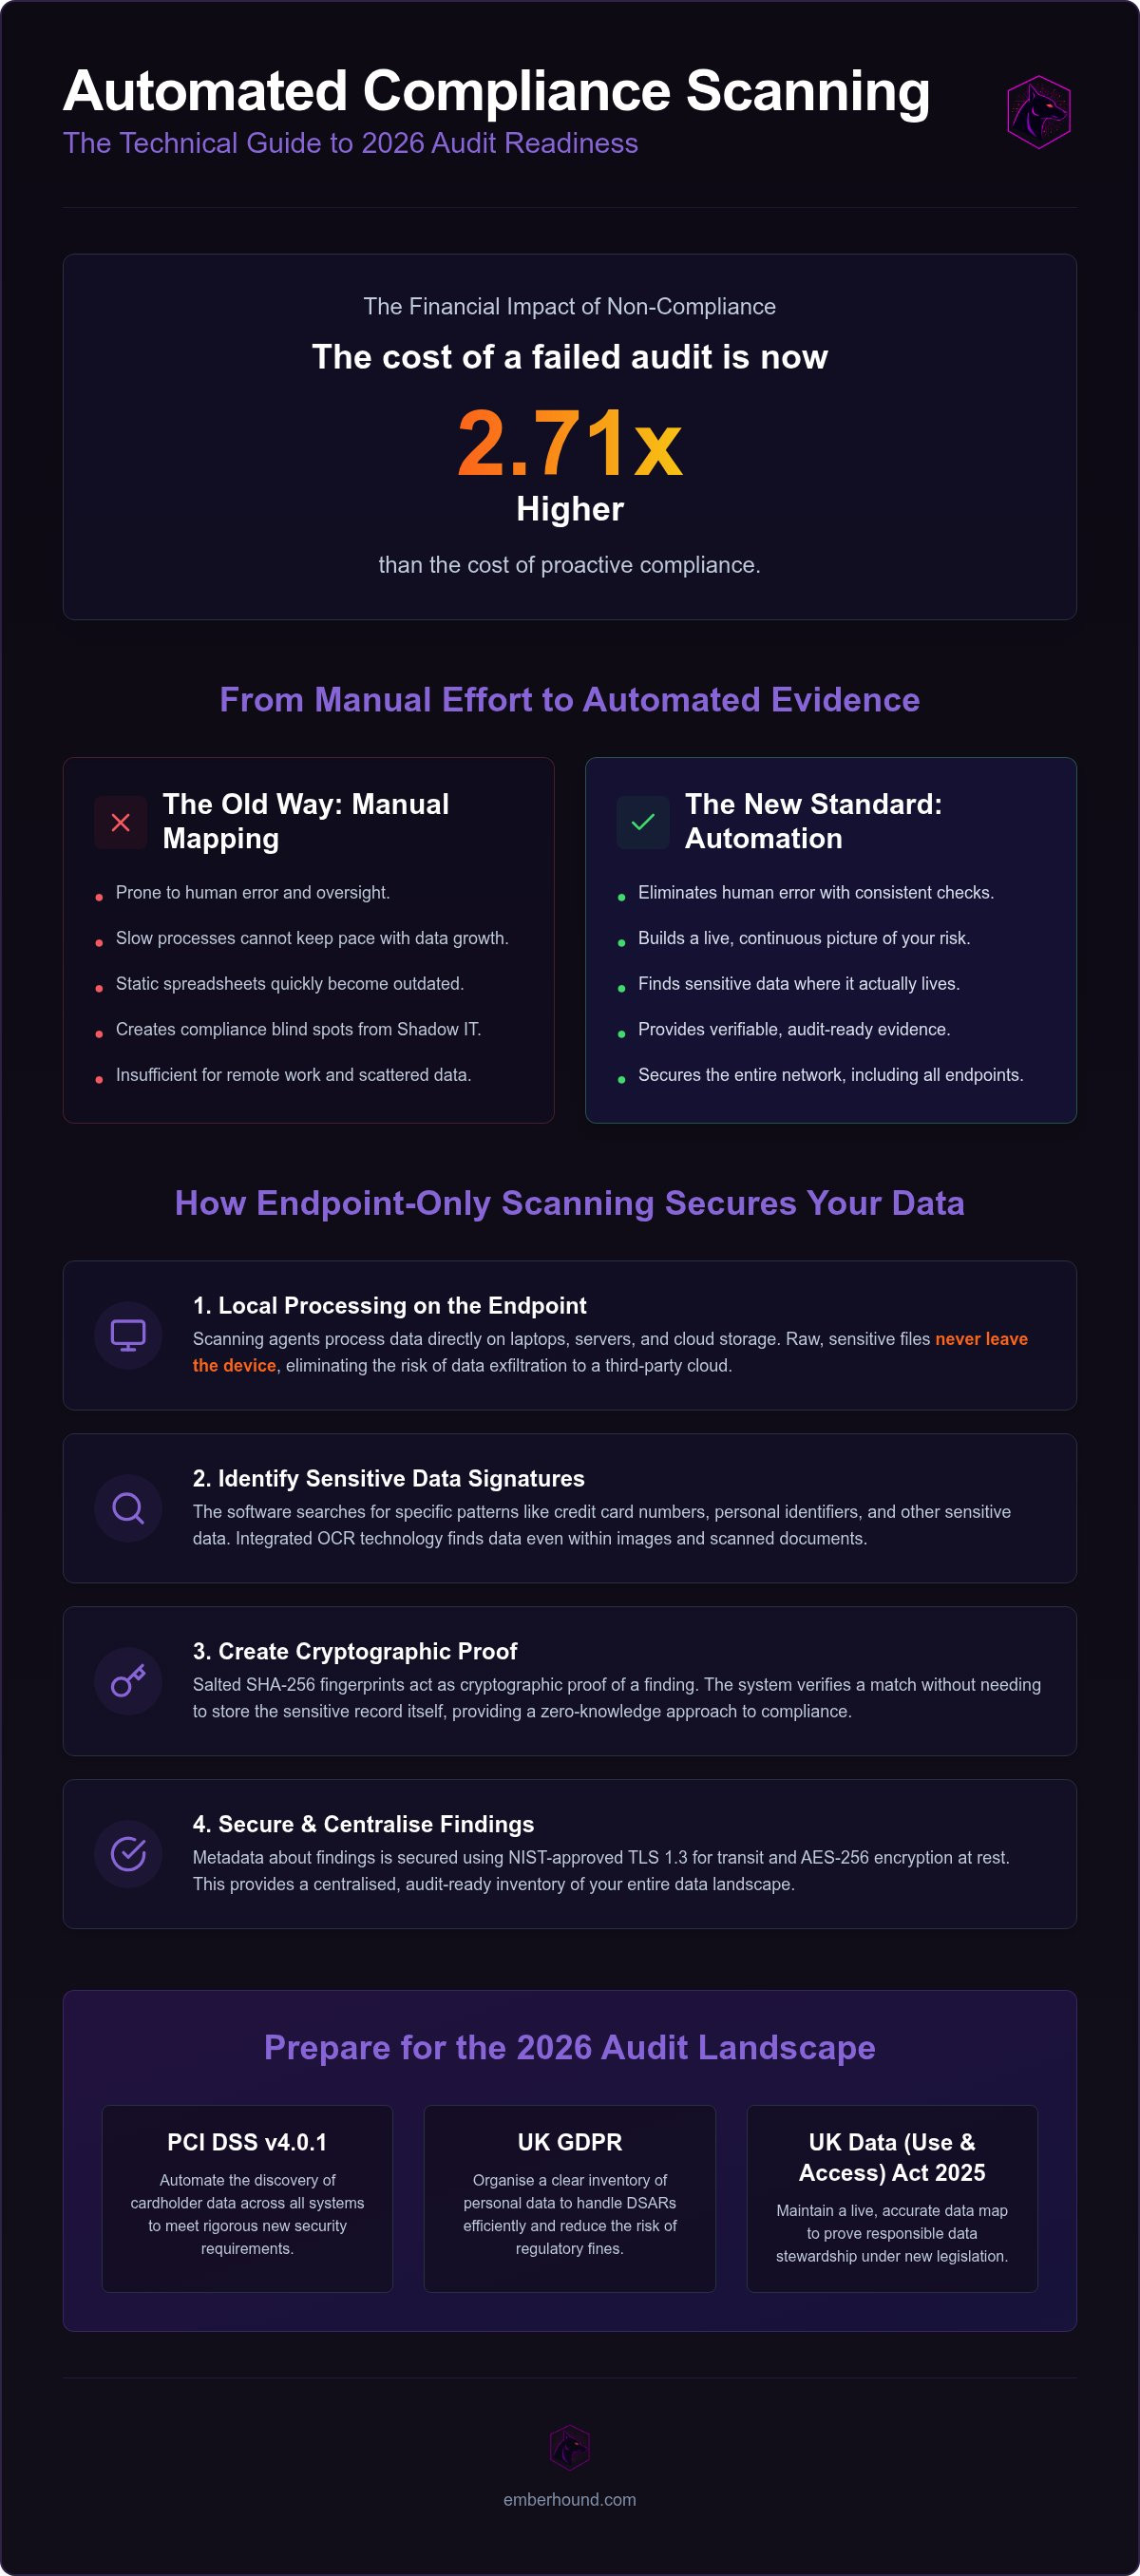
Spreadsheets are static. Data is fluid. Manual mapping fails because it cannot keep pace with 2026 data volumes. Remote work has scattered sensitive data across diverse endpoints. It is in local folders and email attachments. Shadow IT creates hidden repositories of personal data that manual audits miss entirely. When an employee signs up for a new SaaS tool without approval, they create a compliance gap. Automated scanning finds these gaps before a regulator does. It provides visibility where manual effort offers only blind spots.
How automated scanning identifies sensitive data across endpoints
Effective automated compliance scanning software doesn't just look at file names. It examines the bits and bytes on the device. Modern tools use endpoint-only scanning to process data locally. This architecture ensures that raw files never leave the machine. They are never exfiltrated to a third-party server or a central cloud repository. This is a fundamental security requirement. If a tool requires you to upload sensitive files to scan them, it has already increased your risk profile. Local processing eliminates that vulnerability entirely.
The scanning agents look for specific data signatures. They use salted SHA-256 fingerprints to identify matches. This cryptographic approach means the system knows it found a sensitive record without needing to store the record itself. Findings are secured using TLS 1.3 for transit and AES-256 encryption at rest. This standard is approved by NIST and provides the high-level security required for PCI DSS v4.0.1 compliance. It ensures that even the metadata about your discovery remains inaccessible to unauthorised parties.
Endpoint-only processing vs cloud-based scanning
Many legacy tools rely on cloud scanning. This requires constant data movement. It creates a massive attack surface. If the scanning provider is breached, your sensitive data is exposed. Endpoint processing maintains total data privacy. Files stay on the local machine. This method is far more efficient for organisations with large volumes of local files or remote workers on limited connections. It allows for deep inspection of local hard drives and external media without the latency of a cloud upload. It is a direct way to maintain a clean security perimeter whilst performing deep data discovery.
The role of salted fingerprints in audit readiness
Auditors require technical evidence, not just verbal assurances. Salted fingerprints act as a cryptographic proof of work. They allow you to prove a file was scanned and identified without revealing the plain text content to the auditor. It is a zero-knowledge approach to compliance. Masked previews further support this by showing only the necessary characters for internal verification. This protects privacy. It allows your team to confirm a match is legitimate without exposing the full data set. These features provide the audit-ready evidence needed to satisfy regulators under the UK GDPR or PCI DSS v4.0.1 standards. You can run a free scan on your local machine to see how these fingerprints create a secure audit trail without compromising your data.
Essential features for effective data discovery
A basic text search is not enough. To be effective, automated compliance scanning software must parse unstructured data across multiple formats. It needs to look where employees actually hide data - in email chains, image files, and forgotten USB sticks. This requires specific technical capabilities. You cannot rely on a tool that only reads .docx or .xlsx files when the most sensitive information often hides in less obvious places.
OCR scanning for images and PDFs
Many organisations store scans of passports, driving licences, or credit cards as static images. A standard scanner sees these as binary blobs. It cannot read the text inside. OCR (Optical Character Recognition) is a critical requirement for full GDPR compliance. It allows the software to extract text from various image types and identify sensitive data signatures. This includes:
- Scanned passport and ID photos (JPG, PNG)
- Flat PDF documents without text layers
- Screenshots containing credit card data
Without OCR, your data discovery has a massive blind spot that auditors will eventually identify. It is how you find a photograph of a customer's ID card that an employee saved to their desktop instead of a secure server.
Scanning local mailboxes and external drives
Email is the primary source of data leaks. Sensitive data often sits in Outlook attachments for years, long after the original conversation has ended. Effective tools must perform local mailbox scanning to identify these risks. This includes scanning local archives where data is often moved to save server space. Support for external hard drives is equally vital. Backups and portable media often become compliance risks because they are rarely encrypted or properly inventoried. Scanning these devices ensures that your network perimeter isn't the only thing you are protecting. It brings visibility to the "dark data" that exists on the edges of your organisation.
DSAR disclosure pack generation
Subject Access Requests (DSARs) are a heavy administrative burden. Fulfilling one manually can take days of searching through folders, archives, and emails. Modern automated tools reduce this time to minutes. They organise every instance of a person's data into a DSAR disclosure pack instantly. This pack provides the technical evidence needed for a response without the manual labour. It ensures you meet the strict deadlines set by the UK GDPR and frees your team for more productive tasks.
By combining these features, you can run a single scan that addresses both GDPR and PCI DSS frameworks. This unified approach reduces the number of tools you need to manage and ensures that no sensitive data identifier is missed during the discovery process.
Organising an audit-ready data inventory
A data inventory is the bedrock of your security posture. It is a precise record of what sensitive data you hold and where it is located across your network. Without this map, you are flying blind. Automated compliance scanning software generates this inventory automatically during each scan. It replaces the brittle, manual spreadsheets that are out of date the moment they are saved. To remain valid for an audit, your inventory must be a living document that reflects your current environment. A technical data inventory acts as a primary defence during a GDPR audit by providing verifiable proof of data locations and remediation efforts.
Auditors don't want to hear about your intentions. They want to see your results. An automated inventory provides the raw evidence they require. It shows exactly which files contain sensitive identifiers and which endpoints are currently out of compliance. This level of transparency reduces the friction of an audit. It moves the conversation from "how do you know?" to "here is the data."
Mapping data to specific compliance frameworks
Not all data is equal. You must identify which records fall under GDPR requirements and which are subject to PCI DSS v4.0.1. Automated tools can tag data based on the relevant regulation as they find it. This categorisation is vital for prioritising remediation. If you find credit card data on an unencrypted laptop, that is a critical PCI violation that requires immediate action. If you find personal data on a secure server, it may just need a minor policy update. Tagging allows your compliance team to focus their limited time on the highest risks first. It provides the clarity needed to manage diverse regulatory burdens without the need for separate, manual audits for each framework.
Maintaining a continuous compliance posture
Compliance is not a one-time event. It is a continuous process. Your network changes every day. Employees create new files, download attachments, and move data to local folders. You must schedule regular scans to detect these new instances of sensitive data before they become a liability. Use automated alerts to notify your IT team the moment personal data appears in an unauthorised location. This proactive approach prevents small oversights from turning into major breaches. It ensures your organisation stays audit-ready every day of the year, not just the week before an assessment. Regular scanning builds a historical record of your compliance behaviour, which is exactly what regulators look for during an investigation.
EmberHound is the definitive automated compliance scanning software for professionals who have grown tired of deployment drama and corporate bloatware. It provides a precise, accessible platform designed specifically for the constraints of UK SMBs. Our software performs all scanning locally on the endpoint. This ensures your raw files stay private. They never leave your network. It is the smarter, faster alternative to slow-moving enterprise giants that demand cloud access to your most sensitive data. We don't believe in unnecessary complexity. We believe in visibility.Why UK businesses choose EmberHound
We focus on the high-stakes reality of UK compliance teams and Data Protection Officers (DPOs). Our platform is technical yet jargon-light. We avoid the dense, buzzword-heavy "enterprise-speak" that clogs traditional compliance sectors. Instead, we provide audit-ready evidence that satisfies both GDPR and PCI DSS v4.0.1 standards. You get masked previews and salted SHA-256 fingerprints. These prove you have found sensitive data without exposing the actual data to the platform. It is a protective, efficient partnership that respects your constraints.
Small, overworked teams can't afford to waste time on bureaucracy. This is why we offer a usage-based pricing model. There are no mandatory long-term contracts or hidden fees. You pay for the scans you need and nothing more. This transparency is part of our personality as an agile specialist. We don't just point out problems. We hand you the tools to fix them instantly. It is about reducing the burden of complex regulations through immediate, actionable clarity.
Getting started with your first scan
Onboarding is fast. There is no complex deployment drama or months of configuration. You don't need a team of external consultants to get up and running. Simply download the scanner and identify your data risks in minutes. It is a no-nonsense approach to visibility that fits the "lean" professional's grind. If you want to see the platform in action before you begin, watch the EmberHound video demo for a visual walkthrough of the scanning process.
You can start a free scan today. Identify where personal data is hiding across your network before it becomes a liability. Whether it is forgotten email attachments or unencrypted hard drives, EmberHound finds the gaps that manual audits miss. It is about immediate, actionable clarity. Stop worrying about oversight and start building a definitive inventory of your sensitive data. The process is fast, linear, and designed to move you quickly toward results.
Secure your network for the 2026 audit landscape
The landscape of 2026 demands more than just policy documents. It requires hard evidence. Manual data discovery is a gamble you don't need to take. Automated scanning removes the human error that leads to GDPR fines and PCI DSS failures. You now have the technical roadmap to identify sensitive data locally, generate audit-ready inventories, and fulfil DSARs in minutes rather than days. Every forgotten email attachment and unencrypted drive is a potential liability. You can choose to wait for an auditor to find these gaps, or you can find them yourself instantly.
EmberHound delivers this visibility through a Red Dot-calibre interface and usage-based pricing that respects your budget. You get UK-based expert support without the burden of long-term contracts or enterprise bloatware. Modern automated compliance scanning software is the definitive tool for maintaining a continuous security posture. It's about reducing the burden of complex regulations through immediate, actionable clarity.
Visibility is your best defence. Take control of your data and ensure your organisation is ready for whatever the next audit brings.
The tools are ready. The choice is yours.
Frequently asked questions
How does automated compliance scanning software work?
Automated compliance scanning software works by deploying agents to network endpoints to scan local files and folders for specific data patterns. These tools use regular expressions and salted SHA-256 fingerprints to identify sensitive data signatures without needing to read the full file content. By processing data locally on the device, the software creates a map of where personal data resides across your organisation, ensuring you have a live inventory for audit purposes.
Is automated scanning safe for sensitive data?
Automated scanning is safe when it uses an endpoint-only architecture that avoids file exfiltration. Because raw files never leave the machine, the risk of a third-party data breach is eliminated. Secure platforms use TLS 1.3 for transit and AES-256 encryption at rest to protect the findings. Masked previews and salted fingerprints further enhance security by allowing you to verify data matches without exposing the actual sensitive information to the dashboard.
Can automated tools find personal data in images?
Yes, modern automated tools use Optical Character Recognition (OCR) to identify personal data within images and scanned documents. This technology extracts text from JPG, PNG, and flat PDF files to detect identifiers like passport numbers or driving licence details that standard scanners would miss. This capability is vital for GDPR compliance, as many organisations unknowingly store sensitive data in screenshots or scanned ID documents on local hard drives or external media.
What is the difference between data discovery and data mapping?
Data discovery is the technical process of finding and identifying actual files containing sensitive data on your network. Data mapping is the administrative task of documenting where that data should reside and how it flows through your business. Whilst mapping often relies on manual surveys and assumptions, discovery provides the hard technical evidence required for audits. Using automated compliance scanning software ensures your map is based on real-time data locations rather than outdated spreadsheets.
How often should I run a compliance scan?
You should run a compliance scan at least once a month or whenever significant changes occur within your network environment. Data is fluid, and employees frequently create new files or move sensitive information to unauthorised local folders. Regular, scheduled scans ensure that your data inventory remains accurate and that you detect new risks before they lead to a breach. Continuous monitoring is the best practice for maintaining audit readiness under PCI DSS v4.0.1.
Does automated scanning software slow down computers?
Modern scanning software is designed to be lightweight and run in the background without affecting user productivity. Efficient tools manage CPU and memory usage to ensure that the scanning process does not slow down the computer during work hours. By avoiding the bloatware typical of traditional enterprise suites, agile platforms provide deep visibility into local files whilst maintaining the device performance that your team expects for their daily tasks and high-stakes operations.
Is automated scanning required for GDPR compliance?
The GDPR does not explicitly name automated scanning, but it requires you to maintain a record of processing activities and ensure the security of personal data. Under Article 30 and Article 32, you must know where data lives to protect it and respond to DSARs within the legal timeframe. Automated tools are the only practical way to meet these obligations at scale, as manual discovery is too slow and prone to human oversight.


