

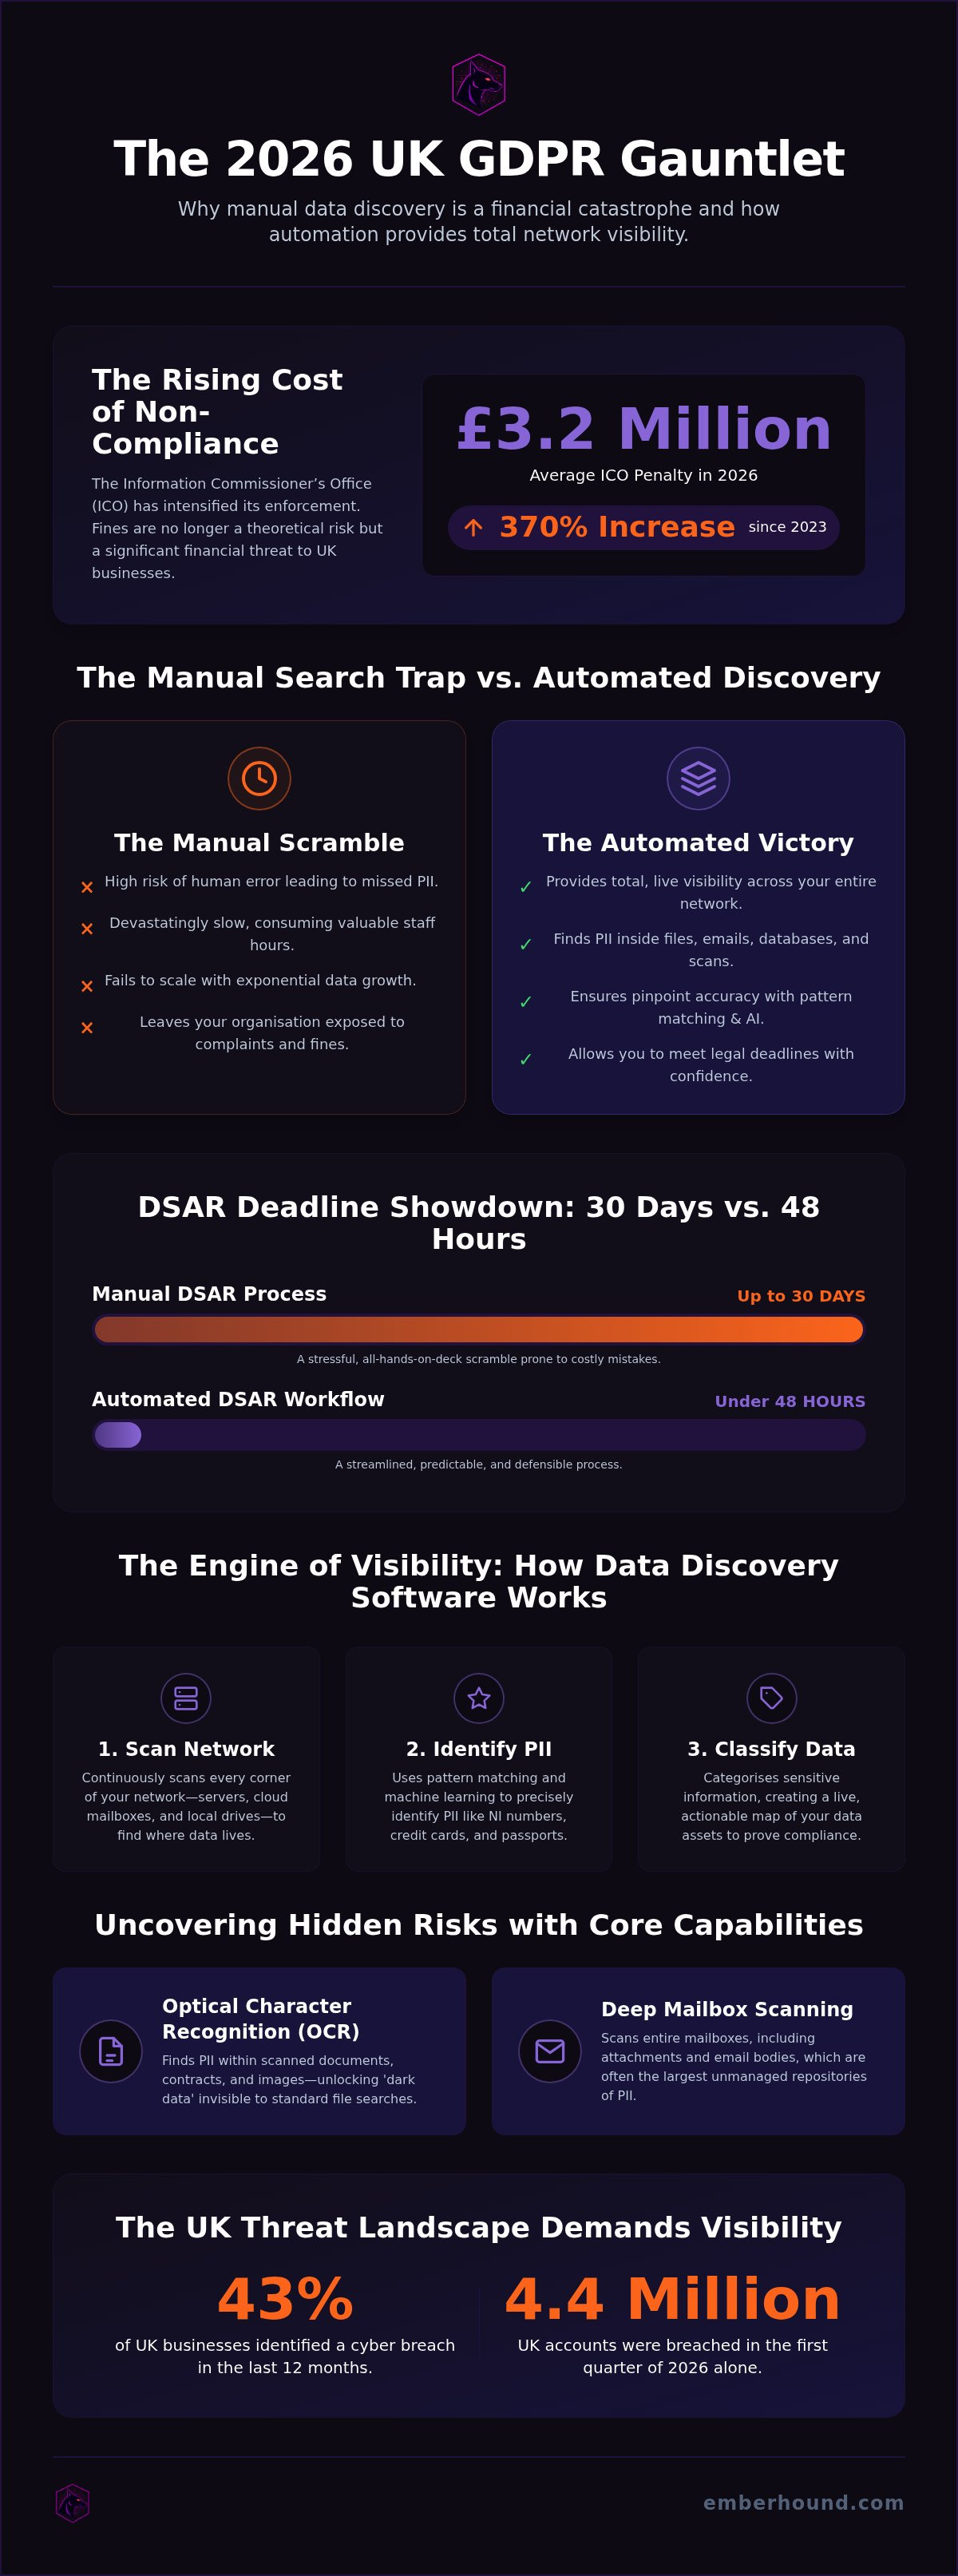
With the average ICO penalty soaring by 370% since 2023 to reach £3.2 million so far in 2026, the cost of "losing" personal data is no longer a theoretical risk. It is a financial catastrophe waiting to happen. You know the panic of a 30-day DSAR deadline. You have felt the dread of searching through thousands of "forgotten" emails and legacy file servers, praying you haven't missed a single scrap of PII. Manual searching is a relic of the past that leaves your organisation wide open to the ICO's aggressive new enforcement regime.
It is time to replace the manual scramble with total network visibility. By deploying the right GDPR data discovery software UK businesses can automate the hunt for sensitive data and turn a month-long headache into a 48-hour victory. You deserve to meet deadlines with ease and face auditors without the usual stress. This guide explores how to locate every piece of PII across your network, navigate the 2026 Data (Use and Access) Act, and prove compliance with absolute certainty.
Key Takeaways
- Understand why manual data searching is a high-stakes liability under the 2026 ICO enforcement regime and how "data bloat" hides PII in plain sight.
- Discover how GDPR data discovery software UK identifies every scrap of personal data across your network using automated scanning and precise pattern matching.
- Learn the critical difference between theoretical data mapping and the practical reality of live data discovery to ensure total visibility of your information assets.
- Master a streamlined 48-hour DSAR workflow that uses dedicated disclosure packs to redact and bundle information, meeting legal deadlines with zero stress.
- Position your lean team for success with UK-based expertise that provides enterprise-grade scanning and OCR technology without the complexity of bloated platforms.
The UK GDPR Challenge: Why Manual Data Discovery is a Risk
Compliance in 2026 is no longer about having a thick folder of policies on a shelf. It's about visibility. The Information Commissioner’s Office (ICO) has shifted its focus from intent to execution. With the Data (Use and Access) Act 2025 now fully operational, the grace period for "organising" your data has ended. If you can't find it, you can't protect it. Most UK businesses are currently drowning in data bloat. They hold vast quantities of Personally Identifiable Information (PII) tucked away in legacy mailboxes, forgotten spreadsheets, and unindexed file servers. This isn't just a storage issue. It's a legal landmine.
Understanding the ICO’s Stance on Data Visibility
The ICO’s expectations have hardened. Claiming ignorance about a forgotten database is no longer a valid defence. Under the current regime, maintaining an accurate Record of Processing Activities (RoPA) requires more than just a best guess. It requires proof. Regulators are increasingly scrutinising data retention policies. They look for evidence that organisations actually delete what they say they delete. Without GDPR data discovery software UK, your RoPA is likely a work of fiction. You need a live view of your data environment to survive an audit. The maximum penalty remains a staggering £17.5 million or 4% of global annual turnover. The stakes are absolute.
The Hidden Costs of Manual Discovery
Manual search is a trap. It feels free because you're using existing staff, but the "per-hour" cost is devastating. When a Subject Access Request (DSAR) hits, your best people drop everything to sift through file servers. They miss things. Human error is inevitable when searching through millions of files manually. Missing a single sensitive document can lead to a formal complaint under the new statutory rights introduced in June 2026. This triggers a 30-day investigation clock that you cannot afford to ignore.
Manual processes simply don't scale. As your business grows, the volume of data expands exponentially. What worked for ten employees will fail for fifty. Relying on manual discovery is like trying to hold back the tide with a bucket. It's slow, exhausting, and ultimately futile. The General Data Protection Regulation (GDPR) and its UK successors demand a level of precision that human hands cannot provide. Oversight leads to more than just fines. It erodes trust with your customers and damages your reputation in a market that increasingly values data privacy. You need a faster, smarter way to stay ahead of the regulators.
What is GDPR Data Discovery Software? The Mechanics of Visibility
GDPR data discovery software UK is the technical engine that powers a modern compliance strategy. It does what human teams cannot: it scans every corner of your network to find, identify, and classify PII. This isn't a simple file search. These tools look inside the documents, spreadsheets, and databases to find sensitive strings of information. They act as an automated auditor that never sleeps. They ensure that your organisation remains aligned with the official ICO guidance on UK GDPR by providing a live map of your data landscape.
The mechanics behind this visibility rely on a blend of pattern matching and machine learning. Pattern matching uses regular expressions to find structured data like National Insurance numbers, credit card details, or UK passport numbers. Machine learning takes this further by understanding context. It can distinguish between a random string of numbers and a sensitive piece of financial data. This is vital because 43% of UK businesses identified a cyber breach in the last 12 months. If you don't know where your data is, you can't protect it from these attacks. Visibility must extend across your entire stack. It isn't enough to scan a single server. Your software needs to reach local hard drives, cloud mailboxes, and legacy archives. With 4.4 million UK accounts breached in the first quarter of 2026 alone, the margin for error is non-existent.
Core Capabilities: OCR and Mailbox Scanning
Many organisations suffer from "dark data" trapped in scanned PDFs or images of IDs. Standard scanners are blind to this. OCR (Optical Character Recognition) technology is the solution. It reads the text within images and extracts it for analysis. This is essential for identifying PII in scanned contracts and employee records. Similarly, mailboxes are often the largest unmanaged repositories of PII. Sensitive data hides in Outlook attachments and forgotten Gmail threads. EmberHound’s OCR and mailbox add-ons ensure that no data remains hidden, providing the "no-nonsense" speed required by lean teams. If you want to see how this works in practice, EmberHound's automated tools provide the clarity you need to stay compliant.
Classification and Labelling
Finding the data is only half the battle. You need to know exactly what you've found. Advanced GDPR data discovery software automatically categorises information into "Standard" PII or "Special Category" data, such as health or ethnicity records. This allows you to prioritise risks. You can see exactly where your most sensitive information resides and take immediate action. The software must provide actionable reports, not just raw data. These reports allow you to prove to auditors that you have a firm grip on your data behaviour and retention policies. It turns a complex regulatory burden into a manageable, automated process.
Data Mapping vs Data Discovery: Choosing the Right UK Tool
Most businesses start their compliance journey with a map. They document where they think personal data lives. This is a dangerous assumption. Data mapping is a theoretical exercise. It is a snapshot in time that becomes obsolete the moment a staff member saves a new spreadsheet to their desktop. It represents where data should be. Data discovery is different. It is the ground truth. It scans your network to show you where data actually resides. For any organisation serious about security, the "should be" is irrelevant. Only the "is" matters.
UK SMEs often fall into the trap of "Compliance Bloatware". These are massive, US-centric platforms designed for global conglomerates with fifty-person legal teams. They are heavy, expensive, and require months of configuration. Lean British teams don't have that luxury. You need to locate PII instantly. By using GDPR data discovery software UK, you skip the endless interviews and manual documentation. You let the software do the heavy lifting. Find the data first. Map it second. This approach eliminates the friction of traditional compliance and ensures your records reflect reality, not just wishful thinking.
Why Discovery Wins During an Audit
Auditors are not interested in your intentions. They want to see your Technical and Organisational Measures (TOMs) in action. When the ICO asks for evidence of your data retention policy, a theoretical map is a weak shield. An automated scan report is an absolute defence. It proves you have a proactive grip on your data behaviour. Discovery tools provide these answers in minutes. Manual mapping takes weeks of staff interviews and guesswork. In the high-stakes environment of 2026, speed is your greatest asset. You cannot afford to wait weeks for an answer that an automated tool can provide before your morning coffee is cold.
Evaluating Software: A Checklist for UK Buyers
Not all scanning tools are created equal. When selecting a partner, look for these non-negotiable features:
- Local UK Support: Does the vendor understand British regulations? Do they operate in your time zone?
- Comprehensive Scanning: Can the tool scan endpoints, cloud mailboxes, and local hard drives simultaneously?
- Unified Coverage: Can it handle PCI Card Data Scanning alongside GDPR requirements? Many UK businesses have both obligations.
- OCR Capability: Can it read PII inside scanned images and PDFs?
Choosing a tool that offers Combined GDPR + PCI Coverage simplifies your security stack. It reduces the number of vendors you manage and provides a single source of truth for your compliance status. Efficiency is the goal. Visibility is the result.
Fulfilling DSARs with Confidence: A 48-Hour Workflow
The 30-day clock is a brutal master. It doesn't care about your workload, your staff shortages, or your current projects. Once a Subject Access Request (DSAR) lands in your inbox, the countdown begins. For many UK businesses, this triggers a month of panic. Teams drop their core tasks to manually sift through thousands of files. It's a recipe for burnout and oversight. However, with the right GDPR data discovery software UK, this process doesn't have to be a crisis. You can shift from a 30-day struggle to a 48-hour workflow that is repeatable, defensible, and stress-free.
As of February 5, 2026, new rules require organisations to conduct a "reasonable and proportionate search" when responding to a DSAR. This is a double-edged sword. Whilst it offers some relief from "infinite" searches, the ICO still expects you to prove that your search was, in fact, thorough. Manual searching rarely meets this standard. Automated tools allow you to reduce the "search phase" from days of manual labour to just a few hours of processing time. You aren't just saving time. You're building a bulletproof audit trail of every search and disclosure performed.
The 48-Hour DSAR Checklist
Efficiency requires a method. Start by identifying the data subject across all network nodes simultaneously. Don't just look in the obvious places. Use your scanning tool to probe mailboxes and hard drives for deep-seated mentions of the subject's name, email, or National Insurance number. Once the data is gathered, use your software to review and redact. You must ensure that you aren't accidentally disclosing third-party data, which is a common way to trigger a secondary breach. By following this structured approach, you can move from request to disclosure pack in less than two business days.
Avoiding Common DSAR Pitfalls
Data often hides in non-obvious places. Sensitive information trapped in image files or scanned ID documents is frequently missed during manual searches. This is where OCR technology becomes your best friend. It ensures that your "reasonable search" includes the dark data that others ignore. Another major risk is over-disclosure. It's tempting to send everything you find to meet the deadline, but this often breaches the privacy of other individuals. A unified DSAR disclosure pack software solution allows you to bundle, redact, and verify information before it leaves your organisation. This protects you from the new statutory right to complain that took effect in June 2026. If you want to stop the manual scramble and start automating your responses, explore EmberHound's DSAR disclosure packs today.
Why EmberHound is the UK Specialist for Lean Compliance Teams
Most compliance platforms are built for global conglomerates with infinite budgets and massive legal departments. They are slow. They are bloated. They are often based in the US, with little understanding of the specific pressures facing British businesses. EmberHound is the UK-based alternative. We are the Agile Guardian for lean teams that need to move fast. Our GDPR data discovery software UK is designed to cut through the noise and deliver immediate network visibility without the corporate fluff.
We don't believe you should manage multiple vendors to cover your security obligations. EmberHound provides a unified scanner that handles GDPR, PCI DSS, and OCR image scanning in a single pass. This combined coverage reduces your operational overhead. It eliminates the need for separate, disconnected tools. Registered in England & Wales (Company No. 17113470), we are a local partner that understands the nuances of the 2026 UK regulatory landscape. We provide enterprise-grade scanning power without the enterprise-grade bill. No-nonsense pricing is at the core of our service. You pay for the visibility you need, not for features you'll never use.
Built for Speed and Visibility
Lean teams don't have months to spend on implementation. You need answers today. We prioritise scanning velocity over complex, unnecessary governance modules. Our tools are designed to be "set and forget." Once deployed, the software works in the background to identify and classify PII across your mailboxes, hard drives, and file servers. Our Mailbox Add on and Hard Drive Add on ensure that every endpoint is covered. Our UK-based support team is always on hand to help you navigate your specific compliance journey. We focus on results, not bureaucracy. We understand the grind of the small, overworked team. We provide exactly what is needed to stay compliant without any distracting extras.
Getting Started: Your Path to Total Data Clarity
You can initiate your first network-wide scan in under an hour. There is no long-winded onboarding process or "consultancy phase." You simply deploy the scanner and watch the data appear. You can customise your compliance packs to focus on GDPR PII, PCI card data, or both. This flexibility allows you to target your highest risks first. Our OCR technology ensures that even scanned contracts and IDs are indexed and searchable. Don't let your data remain a mystery. Secure your data with EmberHound today and take the first step toward total network clarity.
Take Control of Your Data Visibility Today
Compliance is no longer a paperwork exercise. It's a visibility mission. Relying on manual searches in 2026 is a gamble your business cannot afford to lose. With average ICO penalties reaching £3.2 million, the cost of oversight is absolute. The statutory right to complain has turned every DSAR into a high-stakes deadline. You need a solution that finds the truth in minutes, not weeks. By implementing a dedicated GDPR data discovery software UK solution, you move from reactive panic to proactive control.
EmberHound provides the "no-nonsense" speed your lean team requires. With integrated OCR and Mailbox scanning, we uncover the dark data others miss. Our dedicated DSAR disclosure packs ensure you meet every deadline with absolute confidence. You get UK-based support and regulatory expertise without the enterprise-grade complexity. Stop guessing where your PII lives. Start scanning with precision.
Secure your data and automate your UK GDPR compliance with EmberHound. It is time to turn your compliance burden into a streamlined, automated success story. You have the tools. Now, take the lead.
Frequently Asked Questions
How long does a GDPR data discovery scan typically take?
A standard scan typically takes between a few minutes and several hours depending on your network's data volume. Unlike manual searches that drag on for weeks, automated tools process millions of files at high velocity. You get results quickly. This allows you to meet tight 30-day deadlines without the usual last-minute panic. Speed is a technical requirement, not a luxury.
Can GDPR data discovery software find PII in scanned images?
Yes, provided the software includes OCR (Optical Character Recognition) technology. Standard scanners often miss PII trapped inside scanned contracts, IDs, or handwritten notes. Using GDPR data discovery software UK with an OCR add-on ensures these "dark data" repositories are fully indexed and searchable. You gain visibility where others remain blind. It turns unreadable images into actionable compliance data.
Is EmberHound software compatible with UK GDPR and the Data Protection Act 2018?
EmberHound is fully aligned with the requirements of the UK GDPR and the Data Protection Act 2018. Our tools are specifically built to help British organisations maintain accurate Records of Processing Activities (RoPA). We provide the technical measures needed to prove compliance to the ICO. You stay protected under the current UK legal framework with evidence that stands up to an audit.
Does data discovery software impact network performance whilst scanning?
Modern discovery tools are designed to have a negligible impact on network performance. The scanning process is lightweight and can be scheduled during off-peak hours to avoid any disruption to your daily operations. You don't have to choose between operational speed and regulatory compliance. The software works quietly in the background whilst your team stays productive and focused on their core tasks.
How does automated scanning help with PCI DSS compliance?
Automated scanning identifies unencrypted Primary Account Numbers (PAN) and other sensitive cardholder data across your environment. This is a core requirement of PCI DSS. By using GDPR data discovery software UK that includes PCI coverage, you secure your financial data alongside personal information. You eliminate the need for multiple, fragmented security tools and simplify your entire compliance stack.
What happens if we find personal data in an unauthorised location?
You must take immediate action to secure or delete the data according to your retention policy. Finding PII in unauthorised locations is common during an initial scan. The software alerts you to these risks so you can move the files to a secure repository or purge them entirely. This proactive approach prevents a minor oversight from becoming a major breach and a heavy fine.
Do we need a DPO to operate GDPR discovery software?
You don't need a dedicated Data Protection Officer to operate the software. It is designed for lean, multi-tasking teams that need clear, actionable results without deep legal expertise. The tool handles the technical heavy lifting of data identification and classification. This empowers your existing IT or operations staff to manage compliance efficiently and effectively without adding to your headcount.
Is EmberHound a UK-based company?
EmberHound is a specialist UK-based company registered in England and Wales (Company No. 17113470). We focus exclusively on the needs of British businesses and the specific demands of the ICO. You benefit from local support and regulatory expertise that US-centric platforms often lack. We are your local partner in a complex regulatory landscape, providing the "no-nonsense" clarity you need to stay safe.


