

What if your biggest PCI DSS compliance risk isn't in your secure database, but buried in a forgotten spreadsheet on a remote laptop? It is a sobering thought. Most security teams work tirelessly to lock down known payment channels, yet they remain haunted by the "dark data" they cannot see. You know the manual effort required to search through terabytes of files is impossible. The fear of a £50,000 fine for a single oversight is a heavy burden to carry. We understand the pressure of keeping a network clean whilst managing a lean team.
You deserve total visibility. This guide provides a definitive roadmap to find PAN data on network locations you might have overlooked. We will show you how to automate the discovery process and use OCR technology to catch unencrypted numbers hiding in images or scanned documents. By the end of this article, you will have a clear strategy to reduce your PCI DSS scope and walk into your next audit with absolute confidence. No more guessing. No more blind spots. Just a clean, compliant network.
Key Takeaways
- Identify why unencrypted card data is a high-stakes target for breaches and how it compromises your UK regulatory standing.
- Master the exact steps needed to find PAN data on network endpoints, from core servers to the "dark data" sitting on remote employee laptops.
- Move beyond the limitations of manual grep searches and Windows tools that fail to catch unencrypted strings or produce endless false positives.
- Leverage advanced OCR technology to pinpoint sensitive information buried in images and PDFs that standard discovery tools simply cannot see.
- Prepare for your next PCI DSS audit with a streamlined discovery process that reduces scope and ensures no unencrypted PAN remains in plain sight.
Understanding PAN Data and the Risks of Network Exposure
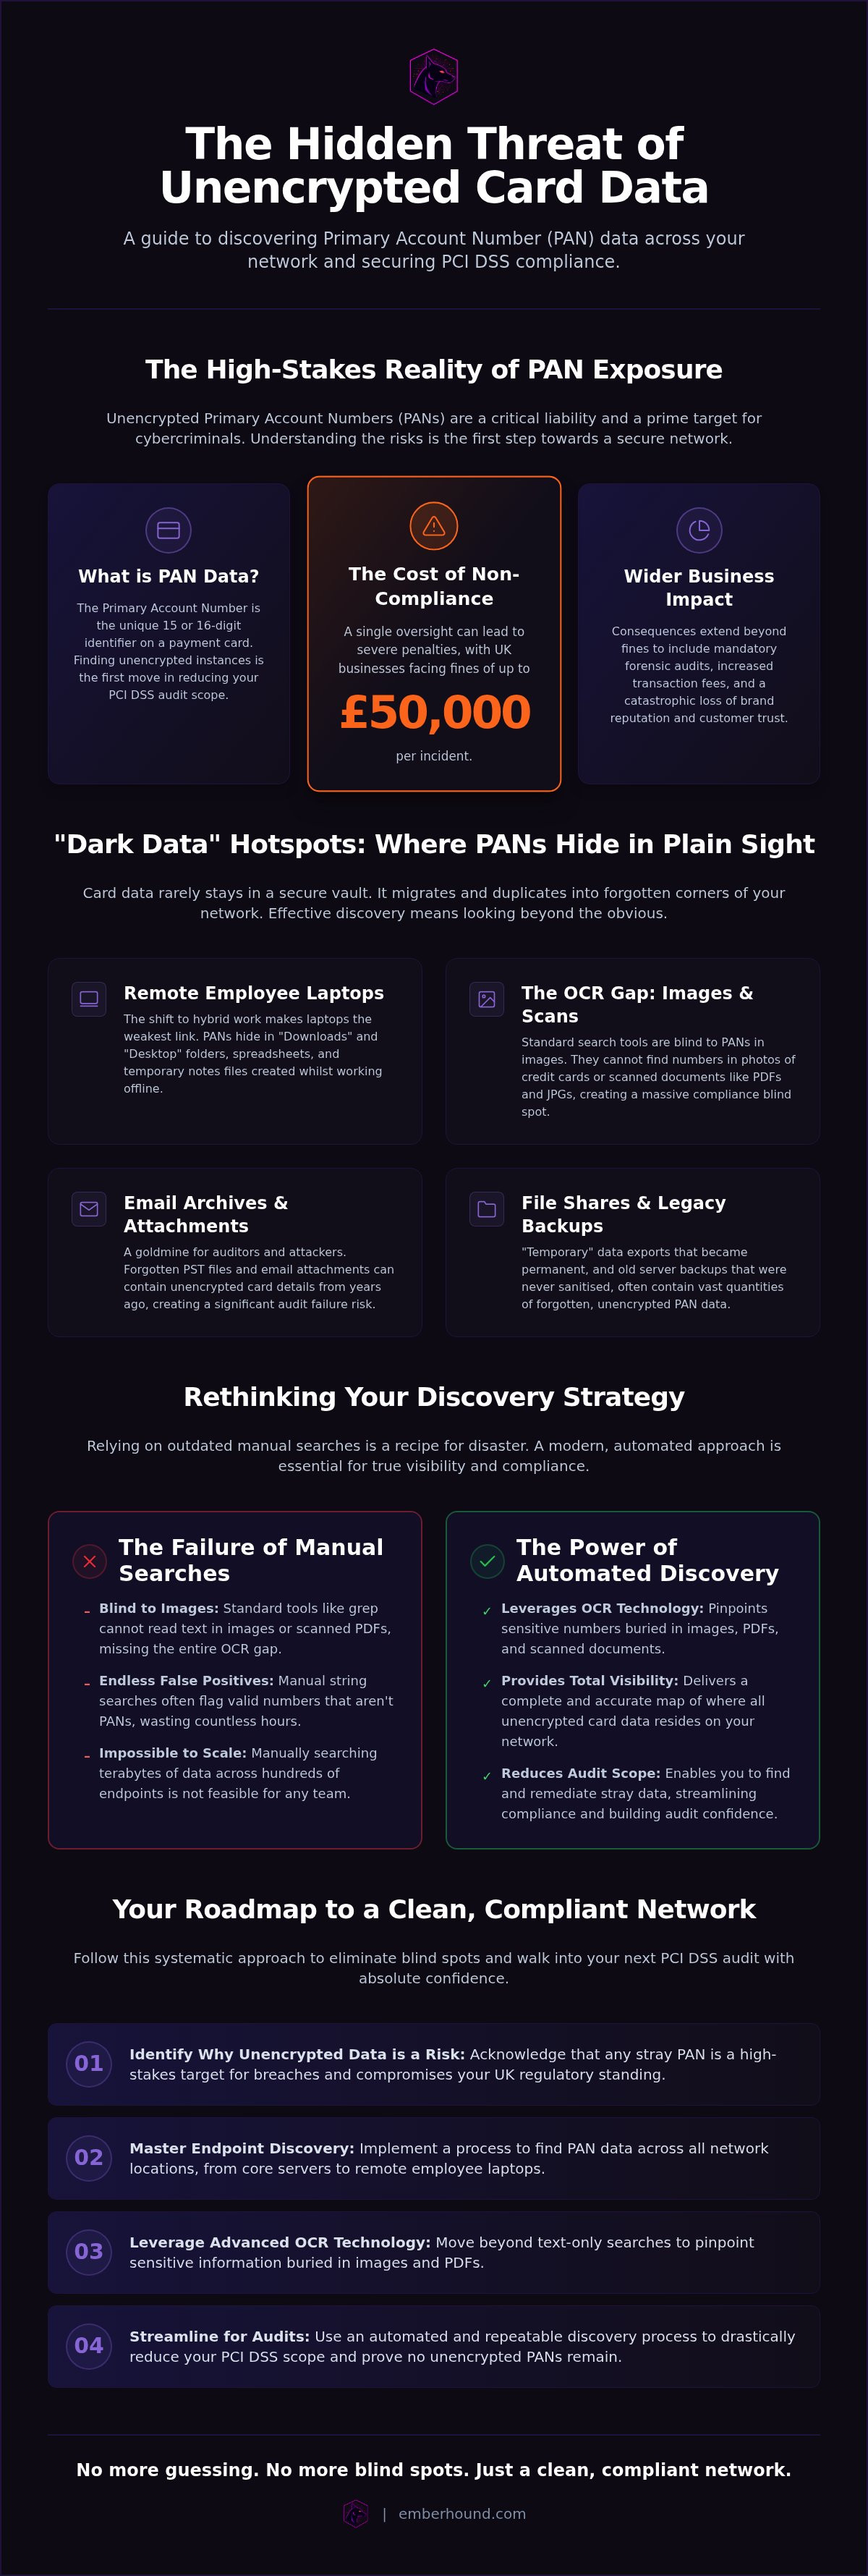
Unencrypted Primary Account Numbers (PANs) are a liability. They are digital gold for cyber criminals. If your business stores cardholder data, you are a target. It is that simple. The problem is that this data rarely stays in your secure vault. It migrates. It duplicates. It hides. Without a strategy to find PAN data on network locations, you are essentially leaving your vault door unlocked whilst assuming your security cameras are enough.
The Definition of PAN Under PCI DSS 4.0
PCI DSS 4.0 defines the Primary Account Number as the unique identifier for a payment card. It is usually 15 or 16 digits. Masking hides most digits for display; hashing turns them into a fixed string for storage. Neither replaces the need to locate unencrypted numbers where they shouldn't exist. Finding this data is the first move in scope reduction. If it is not there, it cannot be stolen. It is the only way to ensure your audit goes smoothly.
Why PAN Data "Leaks" Across Your Network
Data leaks happen in the gaps between processes. A customer service agent might copy a card number into a "notes" file whilst troubleshooting. An accountant might export a "temporary" spreadsheet that stays on their desktop for years. These fragments become "dark data." They hide in file shares, "Downloads" folders, and legacy backups. Your network is likely holding thousands of forgotten numbers in plain sight. You need a way to find PAN data on network endpoints before an auditor does.
UK businesses face more than just fines. A breach can lead to increased transaction fees, mandatory forensic audits costing thousands of pounds, and a total collapse of brand reputation. The financial impact of PCI DSS non-compliance in the UK is often enough to shutter a small firm. You aren't just protecting numbers; you're protecting your livelihood.
Complacency is the enemy. "I thought we deleted that" is the most expensive sentence in compliance. It implies a lack of visibility. You cannot manage what you cannot see. Relying on manual deletion or "good habits" is a recipe for disaster. You need a systematic, automated way to verify that your network is actually clean. Visibility is the only cure for the fear of the unknown.
Where Does Primary Account Number Data Hide on a UK Network?
Finding card data isn't a search task. It is a visibility mission. Most organisations focus their security efforts on central databases and production environments. This is a mistake. Whilst your core systems might be hardened, the data itself is fluid. It leaks. It replicates. To effectively find PAN data on network locations, you must look beyond the obvious repositories and investigate the edge of your infrastructure.
Local Hard Drives and Remote Workers
The shift to hybrid work has shattered the traditional security perimeter. Employee laptops are now the weakest link in your PCI chain. We see it constantly. A staff member downloads a report to their "Downloads" folder for a quick check. They save a spreadsheet to their "Desktop" whilst working offline. This is "shadow IT" in its simplest, most dangerous form. A VPN secures the connection to the office, but it does nothing to protect unencrypted PANs sitting on a local hard drive in an employee's home office. These folders are temporary graveyards where compliance goes to die.
The OCR Gap: PAN Data in Images and Scanned Documents
Traditional search tools are often blind. They look for text strings but ignore pixels. This creates a massive vulnerability. Customers frequently take photos of their credit cards and attach them to support tickets when a payment fails. Accounts departments scan paper invoices and receipts, saving them as flat PDFs or JPGs. Standard grep searches will never find these. You need an unencrypted card data finder that uses Optical Character Recognition (OCR). Without it, you are essentially wearing a blindfold whilst trying to find PAN data on network storage. To stop guessing and start seeing, you can utilise automated scanning tools to map your entire estate.
Email is another major offender. Archived PST files and forgotten attachments are a goldmine for auditors and hackers alike. A single email from three years ago containing a cardholder's details is enough to fail a PCI DSS audit. These files are often buried deep within user profiles; they are invisible to the average user but easily accessible to a sophisticated threat. You cannot assume your network is clean just because your database is encrypted. You have to verify the corners where data hides in plain sight.
The Failure of Manual Searches for PCI DSS Compliance
Manual searching is a trap. It feels productive but it is fundamentally flawed. If you try to find PAN data on network drives using Windows Search or basic Grep commands, you are gambling with your compliance. These tools are designed for general retrieval. They are not forensic instruments. They often skip system files, temporary directories, and compressed archives where unencrypted data loves to hide. Relying on them creates a false sense of security that will crumble during a professional audit.
False Positives vs. Real Threats
Basic search tools are "dumb." They look for patterns but ignore logic. A 16-digit string could be a part number, a tracking ID, or a genuine Primary Account Number. Professional scanning tools use the Luhn algorithm to validate the checksum of a numeric string. This immediately separates the signal from the noise. Without this filter, your team will spend hundreds of hours chasing ghosts. It is a time-wasting cycle that leaves your real vulnerabilities exposed whilst you investigate a harmless spreadsheet of serial numbers.
The Time and Labour Cost of Manual Audits
Consider the scale of modern data. Checking a single terabyte of files manually is a logistical nightmare. Even if a staff member reviewed one file every few seconds, it would take months of uninterrupted work to cover a modern corporate estate. Humans get tired. They get bored. They skip "hidden" folders or assume a directory named "Old Backups" is empty. This is where the 90% of missed data lives. You cannot scale a human-led search to meet the demands of PCI DSS 4.0.
Reclaiming your time is essential. Automated scanning does in minutes what takes a team weeks. It doesn't get distracted. It doesn't skip files. It allows your security professionals to stop being data janitors and start being defenders. When you automate the need to find PAN data on network endpoints, you replace guesswork with actual, verifiable proof of cleanliness. You move from a state of constant anxiety to one of quiet, professional confidence.
A Systematic Approach to Finding PAN Data Across Your Estate
Discovery is not a one-off event. It is a rigorous, repeatable process. To effectively find PAN data on network infrastructure, you must move from reactive searching to proactive mapping. You need a systematic workflow that leaves no stone unturned. Automated discovery is the most efficient way to find PAN data on network endpoints without the burden of manual labour. It replaces guesswork with forensic certainty.
Mapping the Cardholder Data Environment (CDE)
Start by mapping your network topology. You must identify every repository, from primary databases to "dead" archives. There is a critical distinction here: systems that process data and those that merely store it. Discovery is your best tool for scope reduction. If you can prove a server contains no cardholder data, you can move it out of your PCI audit scope. This saves money. It saves time. Don't forget your backups. Legacy tapes and cloud snapshots often harbour the very data you think you've deleted. Once you have mapped the estate, you can deploy PCI card data scanning to begin the deep analysis phase.
Remediation: What to Do Once PAN is Found
Finding the data is only half the battle. You must act decisively. Follow the "Delete First" rule. If there is no business need for the data, purge it immediately. For data that must be retained for legal or operational reasons, use secure encryption. Do not settle for simple password protection. Remediation is about closing the loop and ensuring the same leak doesn't happen twice.
Your remediation strategy should include:
- Quarantine: Move suspicious files to a secure, isolated location for immediate review.
- Encryption: Apply strong cryptographic controls to any data that must be retained.
- Reporting: Create an incident report to understand how the data leaked and improve your internal security posture.
Finally, establish a continuous scanning schedule. Data drift is a constant threat. Employees will continue to save files in the wrong places. New backups will be created. A clean network today does not guarantee a clean network tomorrow. Regular, automated checks ensure that your security posture remains robust between audits. You can organise your network scanning with professional tools to ensure compliance never slips through the cracks. This transition from "one-time fix" to "continuous visibility" is what separates compliant businesses from those waiting for a breach.
Automating Your PCI Discovery with EmberHound
Compliance shouldn't be a full-time manual grind. EmberHound is the no-nonsense UK specialist designed to cut through the noise. We don't do "enterprise-speak" or bloated dashboards. We provide clarity. Our software takes the chaos of a sprawling estate and organises it into actionable intelligence. When you need to find PAN data on network storage, you need a tool that speaks the language of security professionals, not bureaucrats. We understand the constraints of small, overworked teams. We built our tool to be your protective and highly efficient partner.
Rapid Deployment, Immediate Visibility
Setup is fast. You don't have weeks to spend on configuration. Installation to first results happens in minutes, not days. The dashboard is intuitive. It shows you exactly where the risks are without hiding behind complex menus. With our Mailbox and Hard Drive add-ons, your coverage is total. No more dark data on remote laptops. No more forgotten attachments in Outlook. It is visibility delivered at speed. It is about removing friction from your daily workflow.
We offer PCI DSS card data scanning alongside GDPR discovery. This combined coverage provides total peace of mind. Why manage two separate compliance projects when you can handle both from one interface? UK businesses trust our "Efficient Specialist" approach because it respects their time. We identify the problem and give you the tools to fix it instantly. It is about being an agile guardian for your business.
Ready for Your Next PCI Audit?
Walking into an audit without data is a recipe for failure. EmberHound reports provide the concrete evidence PCI QSAs demand. You can prove your network is clean with verifiable documentation. It is the difference between hoping you are compliant and knowing you are. When you use our tools to find PAN data on network locations, you are securing your future. Don't leave your reputation to chance. Take control of your data today. You can book a demo or start your first scan today to see exactly what is hiding in your network.
Secure Your Network and Simplify Your Audit
Manual searching is a relic of the past. It leaves you exposed to fines and oversight. You now know that unencrypted card data hides in plain sight, from local "Downloads" folders to scanned images buried in support tickets. Relying on guesswork is a risk your business cannot afford. To truly find PAN data on network locations across your entire estate, you need a systematic, automated approach that catches what humans miss.
EmberHound is built for lean IT and security teams who need results without the bureaucracy. Our OCR-enabled scanning identifies sensitive data in images and PDFs that standard tools simply ignore. Supported by UK-based compliance experts, we help you reduce your PCI DSS scope and walk into your next audit with absolute certainty. Stop the manual grind and start seeing your data clearly.
Start your PCI PAN scan with EmberHound today. You have the tools. You have the plan. Now, take the final step toward a clean, compliant network.
Frequently Asked Questions
How do I find PAN data on my network without slowing down performance?
You use lightweight, automated agents that throttle resource usage to prevent system lag. Professional tools are designed to scan in the background without impacting user experience or network bandwidth. To effectively find PAN data on network drives without disruption, you should schedule scans for off-peak periods. This ensures your security checks don't interfere with daily UK business operations whilst maintaining total visibility across your entire infrastructure.
Can I find credit card numbers hidden inside image files or PDFs?
Yes, you can locate numbers in images using Optical Character Recognition (OCR) technology. Standard text searches fail here. OCR converts pixels into searchable text, identifying card numbers in scanned receipts, invoices, or photos sent by customers. This closes a massive security gap. Without OCR, your discovery mission is incomplete. It's the only way to ensure unencrypted numbers aren't hiding in plain sight within your document archives.
Is manual searching enough to satisfy a PCI DSS audit in 2026?
Manual searching is insufficient for PCI DSS 4.0 compliance. Auditors require verifiable, repeatable proof that your network is clean. Human-led searches are too slow and prone to oversight. They cannot handle the scale of modern data estates. Relying on a staff member to "check a few folders" won't satisfy a QSA. You need automated logs and reports to provide the forensic evidence required for a successful audit.
What is the difference between PAN and PII in data discovery?
PAN refers specifically to Primary Account Numbers on payment cards, whilst PII covers all Personally Identifiable Information like names and addresses. PAN discovery is a strict PCI DSS requirement. PII discovery falls under GDPR. Whilst they are different, they often overlap. Using a tool that handles both allows you to secure your network against multiple regulatory risks simultaneously. It simplifies your compliance stack and reduces administrative burden.
How often should I scan my network for unencrypted card data?
You should scan your network at least quarterly or after any significant infrastructure change. PCI DSS requirements often dictate regular discovery to prevent "data drift." New files are created every day. Employees move data to unsecure locations without thinking. A single annual scan is not enough. Continuous or frequent periodic scanning ensures that you find PAN data on network locations before it becomes a long-term liability.
Does EmberHound support scanning for remote worker laptops?
Yes, EmberHound provides dedicated support for remote endpoints via our Hard Drive Add-on. The modern UK workforce is hybrid. You cannot ignore data sitting on local laptops just because they aren't in the office. Our software reaches beyond the central server to scan local drives and "Downloads" folders. This ensures your PCI scope covers every device that touches your network, regardless of the user's physical location.
What happens if I find PAN data that we are not supposed to have?
You must follow a strict remediation process: quarantine, investigate, and then either delete or encrypt the data. If you find data you aren't supposed to have, purge it immediately. Document the find in an incident report. This shows auditors that your discovery process is working and that you're taking active steps to improve your security posture. It turns a potential compliance failure into a successful, documented security action.


